OpenAI hack: 3 Indian-origin researchers used Anthropic’s Claude to breach systems
A three-member team of Indian-origin cybersecurity researchers — Mohan Pedhapati and researchers Harsh Jaiswal and Rahul Maini — has demonstrated how an AI-assisted attack could be used to gain access to parts of OpenAI’s internal systems, using Anthropic’s Claude to help exploit a vulnerability in a third-party service.
According to the researchers at cybersecurity startup Hacktron AI and a report by The Wall Street Journal, the team gained access to several OpenAI employees’ ChatGPT and Codex accounts and used one of those accounts to reach OpenAI’s private GitHub environment.
The researchers said they stopped testing after establishing that they could potentially access sensitive internal material. They said they did not read or download OpenAI’s private source code.
WHY IT MATTERS
For the wider AI industry, the episode raises a difficult question -- as AI becomes better at finding and exploiting software flaws, will defenders be able to secure complex systems as quickly as attackers can probe them?
The operation was conducted as part of responsible security research. Hacktron said it reported the vulnerabilities to OpenAI and Discourse, the company whose forum software was involved in the initial vulnerability. OpenAI subsequently paid Hacktron a $6,500 bug bounty.
Here are the LinkedIns of the 3 Indian guys who hacked OpenAI with Opus 5 in 2 days for <$3000:
Rahul Maini, Mohan Pedhapati and Harsh JaiswalNo brand name colleges or companies. Just raw curiosity and skill.
You can just do things. pic.twitter.com/uW3vv3mHlk
— Deedy (@deedydas) September 18, 2026
OpenAI said it fixed the vulnerabilities and revoked affected authentication tokens and sessions.
The incident is significant because the researchers used AI to make the exploit-development process considerably faster. It also shows how a vulnerability in one service can potentially be chained with an authentication weakness to reach other systems.
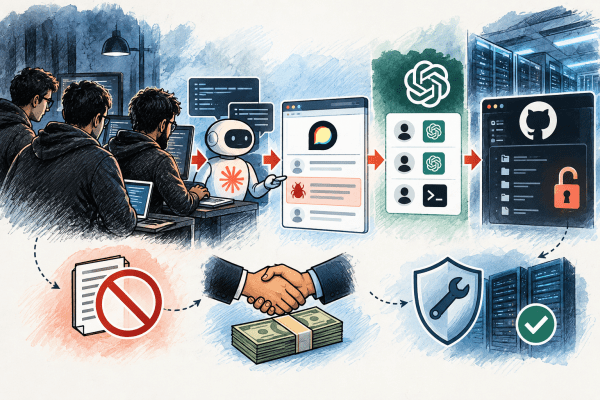 (AI-generated image)
Inside the OpenAI Security Test
Cybersecurity firm Hacktron used AI tools to expose vulnerabilities at OpenAI. Here is what they found, the India connection, and why it matters.
-
✓
Authorised test, not a theftThis was an authorised security test under a bug-bounty process. There is no evidence Hacktron downloaded sensitive source code or accessed model weights.
-
•
How access was provenResearchers proved vulnerability by creating a pull request through a compromised employee's Codex account. OpenAI noted only "limited reads" of private-repository metadata.
-
⚠
The potential reachHacktron noted the potential scope was "huge." Compromised generative AI accounts can be deeply connected to enterprise services like GitHub, Slack, and email.
-
⚡
AI is an accelerator, not a soloistThe incident proves AI reduces the time required to move from finding a vulnerability to exploiting it. However, human researchers still drove the strategy and operation.
-
•
Lowering the barrierExperts warn that generative AI makes sophisticated cyberattack expertise more widely available by helping analyse software and generate attack techniques.
-
•
Industry-wide shiftsFollowing a separate internal breach earlier this year involving Hugging Face, OpenAI reassigned 25% of its production engineers solely to security defense.
-
★
Indian-origin researchersThe Hacktron team responsible for the OpenAI bounty research includes Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini.
-
•
A growing footprintTheir involvement highlights the rapidly expanding overlap between global AI development and cybersecurity—a sector where Indian software and security professionals are highly active.
How did the researchers get into OpenAI?
According to Hacktron’s account of the incident, the research began on July 23, when its researchers were examining OpenAI’s community forum, which runs on Discourse.
Story continues below this ad
The researchers found a vulnerability in the way the forum processed certain HEIC/HEIF image files. Security researchers said the flaw involved the libheif image-processing library used in the image-processing chain.
Hacktron then used Anthropic’s Claude models to help develop an exploit for the vulnerability.
The team said its initial attempts with Claude Opus 4.8 failed to produce a reliable exploit. After Anthropic released Claude Opus 5 on July 24, however, the researchers said the newer model produced a working exploit within hours.
According to Hacktron’s published timeline, the researchers obtained remote code execution on OpenAI’s Discourse-hosted community forum early on July 25. They subsequently submitted their findings to OpenAI and Discourse and continued testing to establish the potential impact.
Story continues below this ad
Mohan Pedhapati, Hacktron’s chief technology officer, told the Wall Street Journal that the researchers were a small team and contrasted their resources with those potentially available to sophisticated state-backed cyber groups.
“I don’t think we are as strong as Chinese threat actors,” Pedhapati said. “We’re just three guys with Claude and Codex subscriptions.”
Hacktron said the experience showed how AI could compress cybersecurity work that previously required considerably more time.
“Work that once required a well-resourced team and months of effort can now be compressed into days,” the company said.
Story continues below this ad
Who are the Indian-origin researchers behind the OpenAI hack?
The Hacktron team comprised chief technology officer Mohan Pedhapati and researchers Harsh Jaiswal and Rahul Maini.
The researchers were working at Hacktron AI, a cybersecurity startup, when they conducted the authorised security research. The team said the OpenAI attack chain took less than 72 hours from the start of their work to demonstrating access to the company’s internal repository.
How did a forum vulnerability lead to ChatGPT accounts?
The initial vulnerability was only the first part of the attack chain. Hacktron said that after gaining access to the forum environment, researchers were able to obtain authentication tokens belonging to users.
Some of those tokens could also be used with OpenAI’s own services. According to the researchers, this included tokens belonging to OpenAI employees, allowing them to gain access to ChatGPT and Codex accounts.
Story continues below this ad
The researchers then discovered that one compromised employee account had access to OpenAI’s GitHub organisation through Codex.
The researchers described this as a separate OpenAI identity or single-sign-on problem rather than simply an extension of the original Discourse vulnerability. VentureBeat, citing Hacktron’s account, similarly reported that the forum acted as the entry point while the account takeover involved an OpenAI identity issue.
In effect, the researchers had chained two separate vulnerabilities: one in the forum environment and another in OpenAI’s authentication infrastructure.
What did they access?
The researchers said they reached OpenAI’s internal software repository, known as Monorepo. The Wall Street Journal, citing people familiar with OpenAI’s architecture, reported that the repository contains important software and algorithmic material belonging to the company. It is not believed to contain OpenAI’s model weights, the numerical parameters at the core of its AI models.
Story continues below this ad
Hacktron said it deliberately avoided examining or downloading sensitive material.
Instead, the researchers used a compromised employee’s Codex account to create a pull request, which is a proposed change to code stored in a repository. The pull request was designed as proof that the researchers had gained access. According to Hacktron, it proposed a harmless change to a documentation file.
The researchers said the proposed change was not accepted. OpenAI’s review found “limited reads” of private-repository metadata and code changes, the company said.
Hacktron said the entire process, from its initial discovery to demonstrating access to the internal repository, took less than 72 hours.
Story continues below this ad
Where did Claude come in?
Claude helped the researchers turn the initial vulnerability into a functioning exploit. Hacktron’s researchers told the Wall Street Journal that AI tools dramatically reduced the amount of time needed to work through the attack.
The researchers clarified that the operation was not carried out entirely using Claude.
They used OpenAI’s own GPT-5.6 Sol during parts of the operation, according to the researchers’ account. The Guardian reported that Claude was used during the initial exploit development, while OpenAI’s model was subsequently used extensively.
AI models developed by competing companies were used at different stages of a security operation targeting OpenAI.
Story continues below this ad
Mohan Pedhapati, Hacktron’s chief technology officer, told the Wall Street Journal that the researchers were a small team and contrasted their resources with those potentially available to sophisticated state-backed cyber groups.
“I don’t think we are as strong as Chinese threat actors,” Pedhapati said. “We’re just three guys with Claude and Codex subscriptions.”
Hacktron said the experience showed how AI could compress cybersecurity work that previously required considerably more time.
“Work that once required a well-resourced team and months of effort can now be compressed into days,” the company said.
What did OpenAI say?
OpenAI confirmed that the researchers had identified security issues and said it had fixed them. “We thank the researchers for contacting us and sharing their findings,” an OpenAI spokesperson said.
The company said it had narrowed the permissions on Community sign-in tokens and revoked affected tokens and sessions.
Discourse separately fixed the underlying forum vulnerability after Hacktron reported it. According to the researchers’ timeline, the issue was reported to Discourse on July 25, and the company subsequently released a fix.
The researchers said OpenAI paid them $6,500 for the OpenAI-side security finding. Hacktron separately reported the underlying Discourse vulnerability to Discourse.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.