「PHP2Shell」脆弱性公表後に悪用試行が数百万件単位に増加したとCloudflareが報告、顧客向けには新ファイアウォールを開発して有効化
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
— Matthew Prince 🌥 (@eastdakota) October 22, 2026
Cloudflareのマシュー・プリンスCEOによると、PHP2Shellを悪用した攻撃試行は情報が公表される10時間前の時点で数千件存在していて、公表から45分後には数万件単位に増加。2時間後には数十万件になり、およそ12時間後には数百万件にまで増加したとのこと。
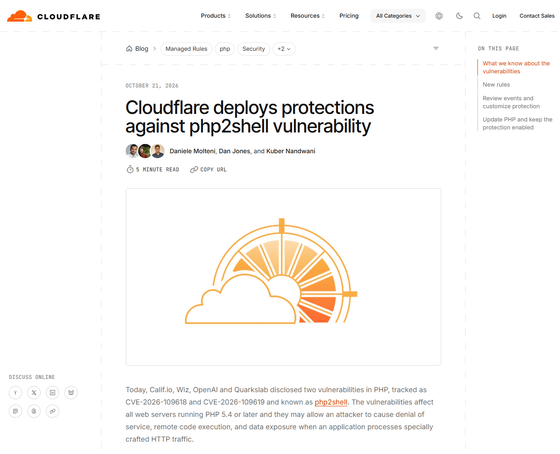
なお、Cloudflareは対策の一環として、2026年10月上旬からウェブアプリケーションファイアウォール(WAF)保護の開発を行い、情報公表のおよそ9時間前に導入して有効化。Cloudflareを無料で利用しているか有料で利用しているかを問わずすべての顧客がPHP2Shellから保護される状態になっているとのことです。
We had to invent a new form of WAF to mitigate this latest set of vulnerabilities. Now enabled by default for all customers for free.
— Matthew Prince 🌥 (@eastdakota) October 21, 2026
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.