No evidence of customer data leak in unauthorized transactions: SinoPac
Bank SinoPac Co (永豐銀行) yesterday said it had found no evidence of customer data being leaked in 427 unauthorized transactions involving 419 customer accounts the previous day.
The transactions resulted from external hackers breaching security settings at suppliers of the bank’s new mobile banking system, the bank said at a news conference to announce the findings of its investigation.
The incident involved 427 transactions, each transferring about NT$100,000 (US$3,050) from Bank SinoPac accounts to a single account at another bank, for a total of approximately NT$41.76 million.
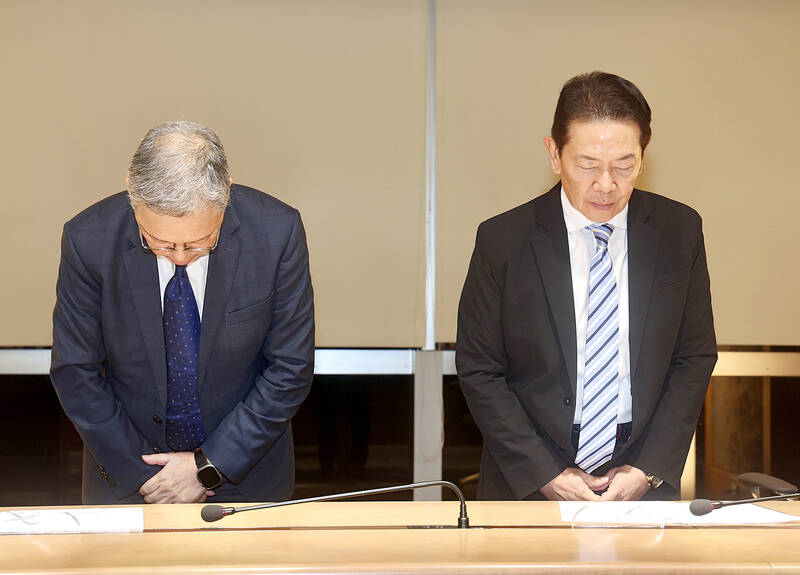
Bank SinoPac Co president Eric Chuang, left, and chairman Tsao Wei-thyr bow in apology yesterday after customer data being leaked in 427 unauthorized transactions involving 419 customer accounts the previous day.
Photo: CNA
The receiving account was temporarily frozen, a Financial Supervisory Commission official said on Tuesday.
The bank said it had immediately reported the incident to authorities after being notified of the irregularities and hired an independent cybersecurity team to identify the source of the breach, contain potential threats and verify the security of its mobile banking and other systems.
The bank said it had found no evidence that personal information had been compromised and had launched additional cybersecurity and data protection checks.
It also confirmed that all affected customers had been reimbursed on Tuesday.
Bank SinoPac said the transaction system through which the unauthorized transactions were made was not used by any other financial institution in Taiwan, adding that it had implemented measures to prevent the same attack method from being used again and strengthened its verification procedures.
The bank said it had also shared relevant information with other financial institutions to help prevent similar incidents.
In addition, Bank SinoPac said it had increased monitoring for suspicious transactions, including measures to promptly intercept unusually large numbers of transfers or inquiries within a short period.
Bank SinoPac chairman Tsao Wei-thyr (曹為實) and president Eric Chuang (莊銘福) bowed and apologized to customers and the public for the anxiety caused by the incident.
Tsao said reimbursing customers would not mark the end of the matter, adding that the bank would continue investigating and implementing improvements to better protect customers’ personal information and assets and regain customers’ trust by improving security.
Chuang said no customers had suffered financial losses but acknowledged that the incident had damaged the bank’s reputation. He added that SinoPac would seek compensation from the system supplier.
The Taipei District Prosecutors Office is investigating the case as a computer security offense.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.