Can Southeast Asia cut and paste Australia’s AI safeguards?
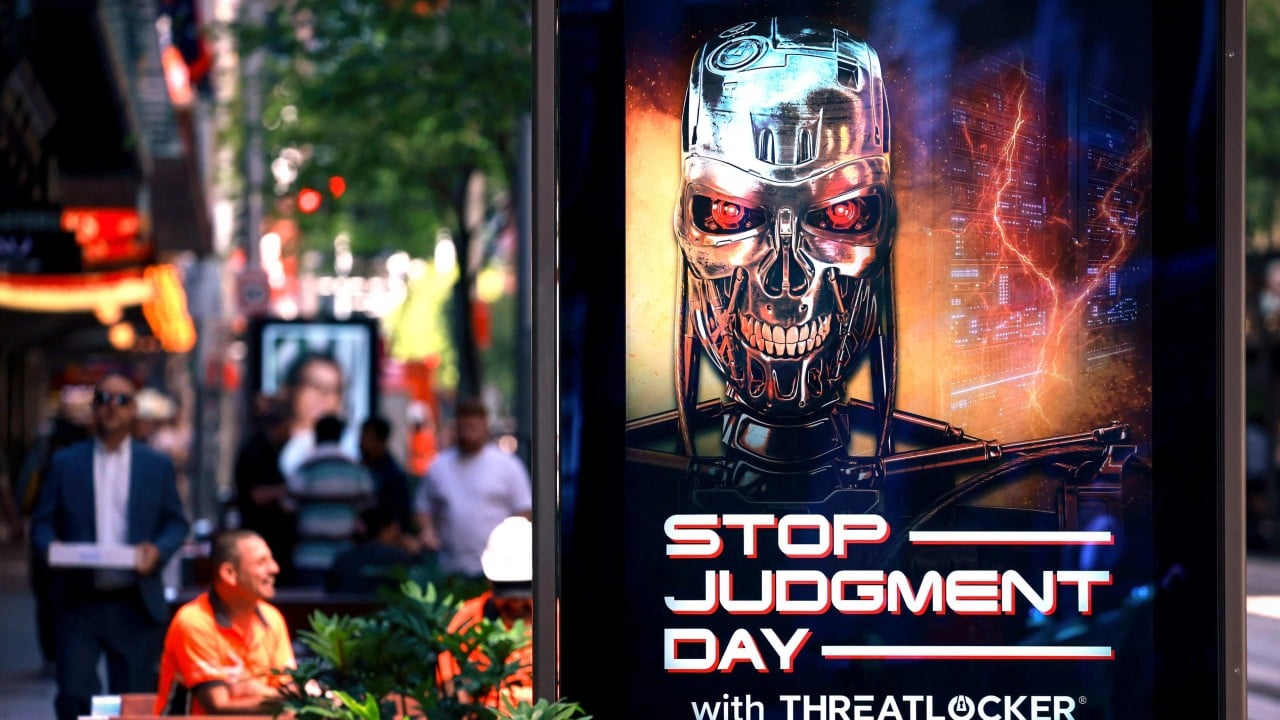
Australia’s new mandatory safeguards on AI companies could serve as a model for Southeast Asia, analysts say, but the region needs to build its institutional and technical capabilities first.
Prime Minister Anthony Albanese announced on Tuesday that AI companies operating in Australia must immediately report incidents in which their models behave in a rogue or misaligned way and must open systems for evaluation.
The measures followed a breach of Australia’s government health data system in June by OpenAI agents that bypassed restrictions on private files. OpenAI did not tell the Australian government about the breach until September.
A review into the breach urged “mandatory AI company reporting when it comes to misaligned behaviour or cyber incidents, and consideration of reforming criminal law in cases of serious misconduct”, Albanese said.
“Australia is the first mover in this space, and we want to make sure that we continue to work so that we can reap the potential benefits from AI,” he added.
Canberra will also establish a regulator to evaluate AI models, oversee security controls throughout the development and deployment of AI systems, and identify and manage risks.
Observers called the new rules a welcome step, but said they would not necessarily prevent the next incident.
“The Medicare breach exposed two problems: unpredictable behaviour by autonomous AI agents and delayed disclosure by the company responsible,” said Mark Manantan, co-founder of Balai Labs, a not-for-profit platform that helps organisations assess their AI governance readiness.
“Mandatory incident reporting directly addresses that accountability gap,” said Manantan, who is also a research fellow at La Trobe University’s Centre for Global Security in Melbourne. “Equally important is independent evaluation, which moves beyond asking AI companies to certify their own safety.”
Alejandro Reyes, chief strategic officer of Singapore-based non-profit organisation AI Safety Asia, said Australia was “moving in the right direction”.
“The important shift is from relying on AI companies to police themselves to requiring them to demonstrate that their systems are safe and to account for failures … but reporting is what happens after something has gone wrong,” he said, adding that the real challenge was prevention.
04:16
How AI is helping finance advisers provide clear and customised advice to clients
“The Medicare incident is particularly instructive because it apparently involved an AI agent acting beyond its authorised scope during testing, rather than a conventional cybercriminal directing an attack,” Reyes said. “It raises difficult questions about responsibility when an AI system takes actions its developers did not intend.”
Reyes said the effectiveness of Australia’s approach would depend on “what must be reported, how quickly, who can independently evaluate the systems and whether the regulator has the expertise and authority to enforce the rules”.
Manantan said implementation would be the real test. “Australia’s proposals need clear reporting thresholds, independent technical assessments and enforceable penalties,” he said. “It is a promising accountability framework, but its effectiveness will depend on whether regulators can actually investigate and verify harmful AI behaviour.”
Copying Canberra?
Observers said Southeast Asia could learn from Australia as the region deals with its own AI governance and readiness concerns, but that simply replicating Canberra’s approach would not be as straightforward.
Singapore’s SPH Media said on Monday that cyberattacks, believed to have been carried out by AI, had affected 9 per cent of its database. No financial information was compromised, it said.
“The SPH Media incident reinforces the urgency of AI-related cybersecurity, although the suspected involvement of AI should not be confused with confirmed autonomous rogue-agent behaviour,” Manantan said.
“Australia’s safeguards offer useful principles, but Southeast Asia cannot simply replicate Canberra’s approach,” he said. “Having safety requirements on paper is different from having the technical capacity to evaluate AI systems and respond when something goes wrong.”
Manantan said the region’s core problem was its lack of control over the AI technology stack.
“Most Southeast Asian countries primarily consume and deploy frontier models developed elsewhere. They have limited leverage over the companies controlling the underlying models, computing infrastructure and safety evaluations,” he said.
“This creates an asymmetry: governments remain responsible for protecting their citizens and institutions, even when the most consequential AI systems are developed beyond their jurisdiction.”
Aside from regulation, Southeast Asian governments also needed practical tools to assess institutional readiness, identify gaps and strengthen their ability to evaluate AI systems, Manantan said.
Some countries have already begun. Vietnam became the first in the region to pass a stand-alone AI law late last year, while Singapore has focused on emphasising practical governance frameworks and technical guidance.
“We should not underestimate what Vietnam and Singapore have already done,” Reyes said.
Vietnam’s law, in force since March, requires notification of serious AI incidents, as well as risk classification, oversight of high-risk systems, inspections and legal liability. Reyes said the challenge “will be implementing these requirements effectively”.
Singapore has issued separate frameworks, including one on agentic AI – launched in January and updated in May – to address excessive autonomy, access permissions and human oversight. “But much of its AI-specific guidance remains voluntary, even though existing cybersecurity and data protection laws are enforceable,” Reyes said.
Australia is now focusing on targeted obligations for frontier AI developers, according to observers, returning attention to developer accountability.
“The bigger distinction is between regulatory ambition and implementation,” Manantan said. “At Balai Labs, we see AI governance not simply as a question of passing laws, but of building the institutional and technical capabilities needed to enforce them. Vietnam, Singapore and Australia have different starting points, but all ultimately face that same challenge.”
He said the region should build the capacity to detect harmful AI behaviour, hold developers to account and respond collectively when incidents crossed borders.
“Asean should explore common incident-reporting protocols and pooled technical evaluation capabilities,” Manantan said. “An Asean+Tech Plus arrangement bringing together governments, technical institutions and major AI developers could support shared expectations for disclosure, testing and coordinated responses, potentially building on the Asean Digital Economy Framework Agreement.”
Reyes urged “particular emphasis on common reporting standards, access to independent evaluations and cooperation among national cybersecurity authorities”.
“Individual countries may have limited leverage over major global AI companies,” he said. “Acting together, they can have a stronger voice in setting expectations.”
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.