CPI(M) MP seeks independent probe into SBI customer data exposure, writes to FM Nirmala Sitharaman
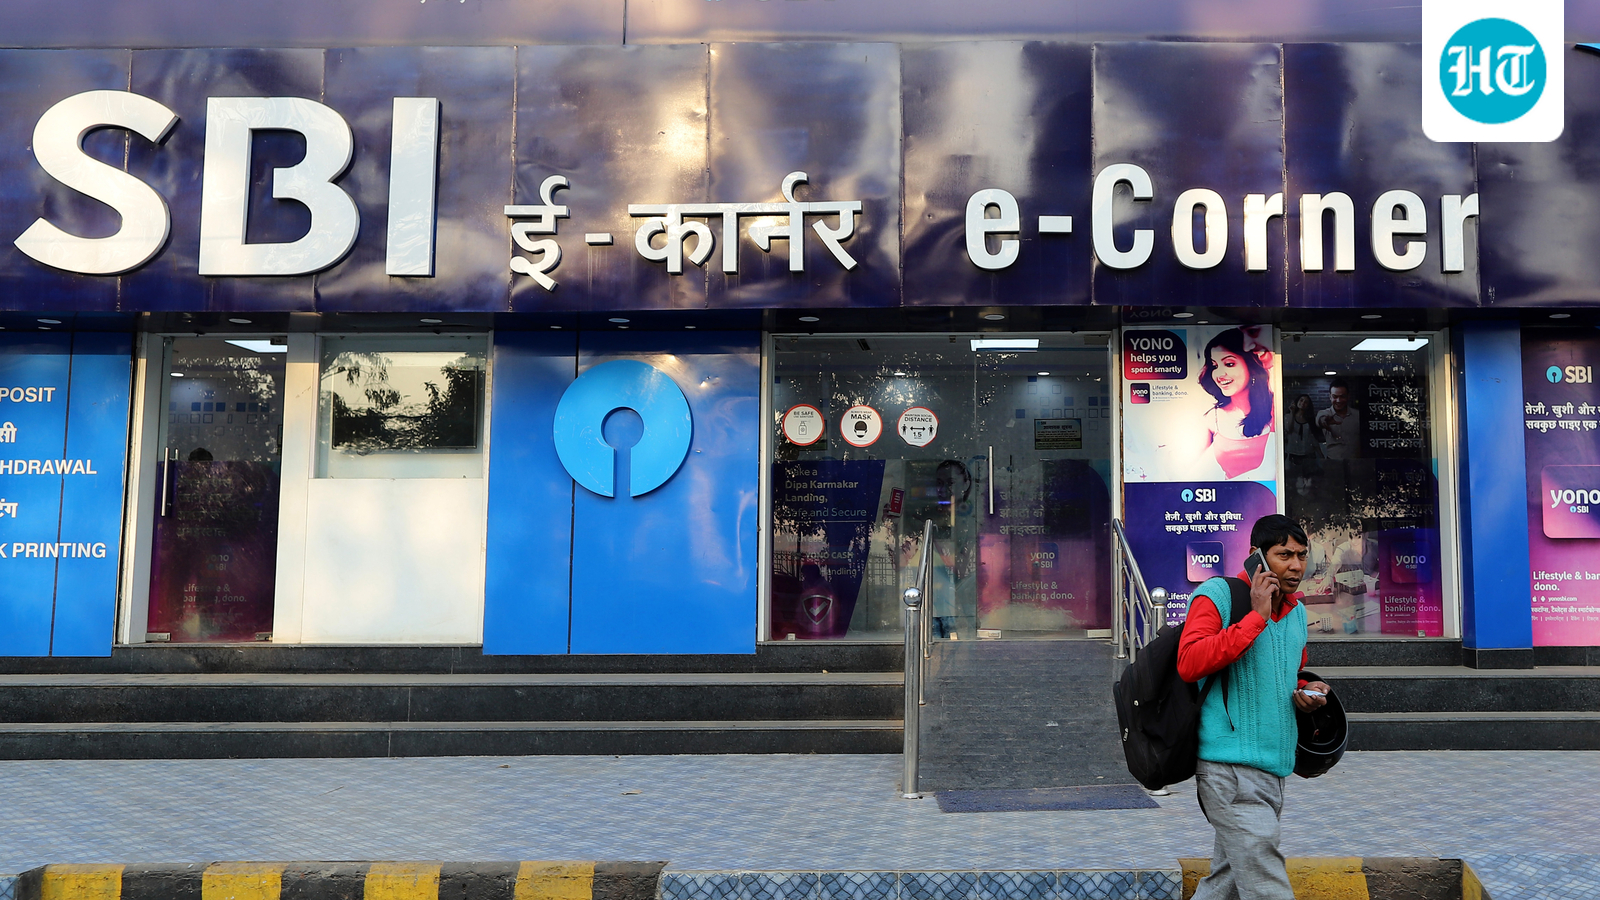
CPI(M) MP A A Rahim wrote to Union finance minister Nirmala Sitharaman, seeking an independent investigation into the reported exposure of 3,897 State Bank of India (SBI) customer records on the dark web.
He urged the state-run bank to notify affected customers directly and asked the Centre to take urgent measures to safeguard them, in addition to “strict accountability” for security lapses.
“Wrote to FM Nirmala Sitharaman on the alarming exposure of SBI customer data on the dark web. I urge an independent probe, direct notification to affected citizens, and strict accountability for security lapses,” Rahim said in a post on X, sharing the letter dated October 21.
The SBI data exposure
On October 21, SBI informed the Bombay Stock Exchange and the National Stock Exchange that it had suffered “an incident involving the loss of certain data,” with 3,897 customer records containing personal information identified in a larger trove of about 3.75 lakh records on the dark web.
The exposed information reportedly included registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and Customer Information File (CIF) identifiers, lead IDs, and metadata linked to loan records and other files.
The bank said it learnt of the incident on October 16 through its threat intelligence provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In).
What the CPI(M) MP said in letter to Sitharaman
In his letter, Rahim said the incident raised concerns about the adequacy of data protection and cybersecurity safeguards at public-sector banks. He stressed the need to ensure that institutions entrusted with citizens’ financial security adequately protect their personal information.
“While the bank has indicated that its core operations remain unaffected, the absence of disruption to banking services does not diminish the seriousness of the potential compromise of customers’ personal information,” Rahim wrote, stressing that the incident’s implications extended beyond its impact on the bank’s operations.
He urged the finance ministry to ensure a comprehensive and independent investigation, with clear timelines to identify the source and extent of the suspected breach. “SBI should take immediate steps to directly notify all affected customers through accessible channels for reporting suspected fraud, and extend appropriate assistance to those at risk,” he added.
Rahim warned that customers whose personal information had been exposed could face identity theft, targeted phishing, impersonation and financial fraud. “Customers must not be left exposed to fraudulent calls, impersonation and other forms of exploitation without timely information and adequate institutional support,” he wrote.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.