‘000000’ dethrones ‘123456’ as Malaysians’ top password despite surging hacking fears
The password “000000” turned up more than 120,000 times among online users in Malaysia over a year to September, according to a global study, overtaking “123456” as the country’s most common exposed password amid a recent wave of data leaks.
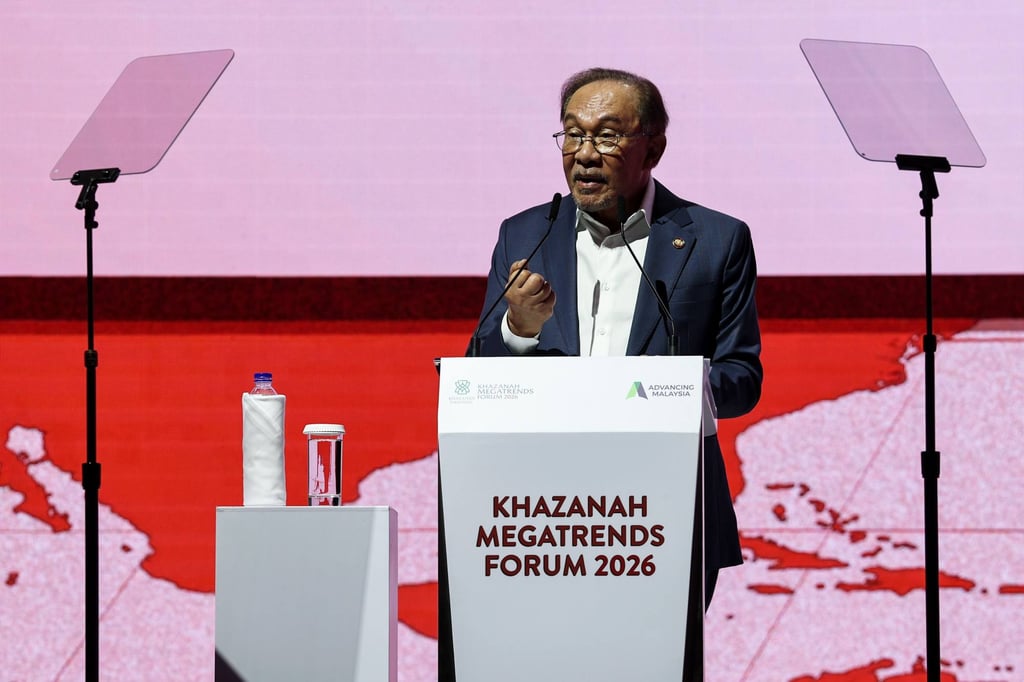
The findings come as Prime Minister Anwar Ibrahim calls for a review of cybersecurity across government agencies, banks and state-linked companies. Malaysia raised its national cyber threat level from low to medium earlier this month, days before hackers defaced the website of its largest Islamic cooperative bank.
Password manager NordPass and threat-exposure firm NordStellar, both part of Lithuanian cybersecurity group Nord Security, conducted the study covering 44 countries based on an analysis of passwords exposed between September 2025 and September 2026, with researchers examining public data breaches and collections of leaked passwords circulating on the dark web.
Globally, “123456” kept its top spot, ahead of “admin” and “12345678”. In Malaysia, researchers counted 120,617 instances of “000000”, against 83,896 for “123456”, while “111111” took third place. Half of the Malaysian top 20 consisted entirely of numbers, and the word “password” came in 11th.
Malaysian cybersecurity practitioner Murugason R. Thangaratnam said the ranking depended heavily on “which services were compromised and what those services allowed”.
“Many of these platforms are older, lower-priority or numeric PIN-style services where convenience was designed in, and security was not,” he said.
“If a platform accepts a six-digit string of zeros, or has no minimum length, no complexity check and no screening against known compromised passwords, then it has effectively approved that choice.”
Email was his first concern because it was “the master key” and “whoever controls it can reset almost everything else”.
He also pointed to shopping and delivery accounts that stored home addresses and card details, and social media accounts “that scammers hijack to impersonate victims and cheat their contacts”.
Beyond bank protection
Malaysia’s National Cyber Security Agency recorded 5,110 cybersecurity incidents in the first nine months of this year, its chief executive Megat Zuhairy Megat Tajuddin told state news agency Bernama on November 9.
Authorities instructed operators of critical infrastructure on November 7 to monitor their systems around the clock and require a second means of verifying a user’s identity, a day after hackers defaced the corporate pages of Bank Rakyat.
The bank, which held 131 billion ringgit in assets at the end of last year, later assured customers their deposits and personal data were safe after its corporate website became inaccessible.
Communications Minister Fahmi Fadzil said hackers had altered the appearance of the site, run by an external provider engaged by the bank.
“So our banking and financial sectors remain secure, and online transactions are safe,” Fahmi said.
Fong Choong Fook, founder of Malaysian cybersecurity firm LGMS, said many business owners still assumed hackers were mainly interested in banks.
“So a lot of the time, when some devices are being set up, we never bother to change the default password,” Fong said.
He added that in his 30 years in cybersecurity, he had “never seen so many successful attacks, successful compromises that all happen at the same time” as he had in recent months.
“Many of them do not think about prevention. That’s again normal human behaviour. They always think that disaster only happens to somebody else, not them. But by the time they get hit, it’s going to hit pretty bad,” he said.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.