NSB probes hack on Puma Shen
SUSTAINED ASSAULT: The attacks, which began on Friday last week, exploited a flaw to gain administrative access to the host server, Shen’s office said on Wednesday
By Kan Meng-lin, Huang Ching-hsuan and Jonathan Chin / Staff reporters, with staff writer


The National Security Bureau (NSB) is investigating suspected cyberattacks originating from China that targeted Democratic Progressive Party (DPP) Taipei mayoral candidate Puma Shen (沈伯洋), a top official said yesterday.
“The bureau is doing all within its power to ensure the [Nov. 28] elections will be carried out safely and smoothly,” NSB Deputy Director-General Chen Sung-chi (陳松吉) told a meeting of the legislature’s Foreign Affairs and National Defense Committee in response to a lawmaker’s question about the alleged hack.
NSB intelligence teams are conducting a joint investigation into China’s alleged meddling in the election that could lead to criminal charges against those found responsible for the attack, he said.
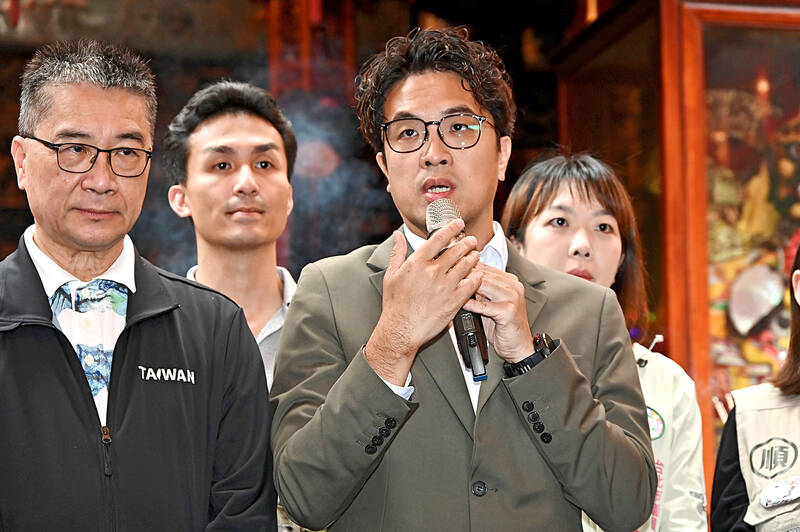
Democratic Progressive Party Taipei mayoral candidate Puma Shen, second right, speaks at Songshan Ciyou Temple in Taipei yesterday.
Photo: Tu Chien-jung, Taipei Times
Shen’s office late on Wednesday said it has detected evidence of “planned and sustained” cyberattacks on its key digital infrastructure, including the internal system used by staff and public-facing Web sites.
The attacks, which started on Friday last week, exploited a flaw in the site’s upload function to gain administrative access to the host server, allowing the hackers to install back doors, it said.
The hackers were foiled in their main objective of accessing the campaign’s internal system, as the compromised server did not host that system or its log-in credentials, the office said.
The campaign detected the attack on Wednesday morning and took countermeasures to repair the damage, including deleting the back doors and fake admin accounts, changing all credentials and hardening its systems’ cybersecurity, the office said.
Hackers continued to target Shen’s campaign, including a denial-of-service attack on a new Web site the campaign rolled out the same day, it said.
The site, designed for supporters to swipe in during the campaign’s “Ocean Wave” (洋流) events, received more than 70,000 requests for authentication codes from out-of-country IP addresses within an hour of going online, it said.
The administrators altered the site’s swipe-in function to require logging into the system with a valid account, which halted the attacks, the office said.
“The campaign is using the highest cybersecurity standards to ensure election integrity,” it said. “All Web sites and pages that had come under attack were restored and hardened ... to defend them against external malicious forces.”
Shen told reporters on the sidelines of the legislative meeting that the attempt to hack into the campaign’s system failed because his team takes cybersecurity seriously.
The timely actions of the staff running the “Ocean Wave” map have prevented an attack that could potentially have paralyzed the campaign’s platform, he said.
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.