Critical PHP flaw forces Web sites worldwide offline, sparks cyberattack fears PHP爆重大資安漏洞 全球網站緊急下線防駭客攻擊
Web sites around the globe have gone dark after a serious vulnerability was found in a computer language used to build much of the World Wide Web.
Belgian, Dutch, Finnish, French and German sites were among those that governments took down temporarily as they scrambled to patch the critical weakness in PHP, a language used by almost 70 percent of Web sites.
The vulnerability in the programming language, which became public on Tuesday last week, sparked warnings from national security agencies in Washington and London. It means millions of Web sites will need to be fixed. One Internet infrastructure expert said Russian state actors or organized criminals could exploit the flaw to carry out cyber-attacks.
“Cyber Attack Detected” phrase and PHP code appears in this illustration taken Oct. 22. 10月22日所攝之示意圖顯示「偵測到網路攻擊」字樣及PHP程式碼。
Photo: Reuters 照片:路透
WordPress, one of the most common Web site systems, uses PHP, as does Wikipedia, the messaging software Slack and — at least historically — much of Facebook. The Wikimedia Foundation said it had taken down several systems on Wednesday last week as a precautionary measure until they could be patched.
The organization behind the language issued a patch on Wednesday last week after researchers testing cyberdefences discovered the flaw. The US National Security Agency told all organizations using PHP to take their systems offline if they were unable to patch them immediately. It said the vulnerability could “provide a direct path to the server’s file system or database.”
Because a fix is now public and AI tools are able to reverse engineer the bug with little effort, experts said they were bracing for a wave of intrusions as hackers jumped to get ahead of the updates.
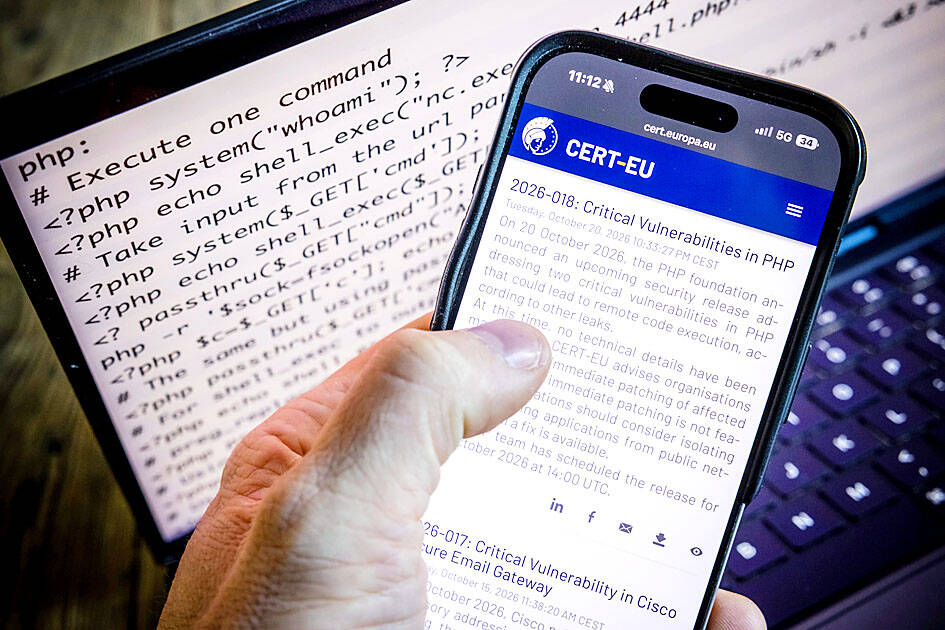
The Web site of the Computer Emergency Response Team for the EU Institutions, Bodies and Agencies (CERT-EU) is displayed on a mobile phone in Mierlo, the Netherlands on Oct. 21. 一支手機螢幕顯示歐盟電腦網路危機處理中心(CERT-EU)之網站。10月21日攝於荷蘭米爾洛。
Photo: EPA 照片:歐新社
AI was powering a “race to exploit,” said Costin Raiu, co-founder of cybersecurity research and incident response firm TLP:Black. He said the next step was the “mass compromise of every vulnerable web server on the Internet.”
OpenAI said it led a coalition of researchers that discovered the flaw and claimed “frontier AI” had been key. The researcher who found the weakness, however, said they used models available to the public.
Cybersecurity company Calif said in a blog post it found the flaws with the help of a large language model on Aug. 1 and had been working on a fix ever since. Alphabet-owned cybersecurity company Wiz said in a blog post that it too had discovered it with the help of Wiz Atlas, its autonomous AI vulnerability research tool, as well as Google’s Gemini 4 Argon and OpenAI’s GPT-5.6 Sol.
An illustration taken on Oct. 21 shows a padlock in front of binary code on a laptop screen in Frankfurt am Main, Germany. 鎖頭圖樣置於筆記型電腦螢幕上之二進位程式碼前。10月21日攝於德國法蘭克福。
Photo: AFP 照片:法新社
The vulnerabilities remained hidden in the PHP codebase for more than a decade and would have been extraordinarily complicated for a human hacker to take advantage of, Wiz’s post said.
Michal Wozniak, an Internet infrastructure expert, said: “There’s going to be a lot of automatic exploitation of this.” The bug might allow cryptocurrency miners to exploit vulnerable servers at other people’s expense, he said.
He also said large crime organizations and Russian state actors could use the vulnerable sites as a launching pad from which to conduct distributed denial of service (DDoS) and other cyber-attacks.
The issue highlighted the poor state of Internet infrastructure, Wozniak said, something that was being brought to light by advancing AI models but that had been a long-developing problem. The underlying vulnerabilities the researcher found were decades old.
“This is an environmental problem in an industry where there’s an incentive to move fast and make changes,” he said. “There’s an incentive to deploy a thing and then never update it and not think about maintenance.”(The Guardian)
由於廣泛用於架設全球資訊網的程式語言發現嚴重安全漏洞,全球多地網站紛紛暫時關閉。
比利時、荷蘭、芬蘭、法國及德國等國的部分網站,都因政府緊急修補PHP程式語言的重大安全漏洞而暫時下線。PHP是全球近七成網站使用的程式語言。
PHP程式語言的漏洞上週二曝光後,美國華府與英國倫敦的國家安全機構紛紛發出警示,意味全球數百萬個網站都必須進行修補。一名網路基礎設施專家表示,俄羅斯國家級駭客或組織犯罪集團可能會利用這個漏洞發動網路攻擊。
全球最普遍使用的網站建置系統之一WordPress採用PHP,維基百科(Wikipedia)、通訊軟體Slack,以及Facebook過去的大部分系統,也都使用PHP語言。維基媒體基金會(Wikimedia Foundation)表示,已於上週三預防性關閉數個系統,直到完成漏洞修補為止。
研究人員在測試網路防禦系統時發現這個漏洞後,PHP開發團隊於上週三發布修補程式。美國國家安全局(NSA)呼籲所有使用PHP的機構,若無法立即修補漏洞,就應將相關系統暫時下線。NSA指出,這項漏洞可能「讓攻擊者直接存取伺服器的檔案系統或資料庫」。
由於修補程式已經公開,加上人工智慧(AI)工具能夠輕易逆向分析漏洞,專家表示,正準備因應可能接踵而來的大規模入侵行動,因為駭客正爭相在系統更新完成前發動攻擊。
網路安全研究與事件應變公司TLP:Black共同創辦人科斯汀.拉尤表示,AI正在推動一場「漏洞利用競賽」。他說,接下來可能出現的情況,是「網際網路上所有存在漏洞的網頁伺服器遭到大規模入侵」。
OpenAI表示,由該公司領導的研究團隊聯盟發現了這項漏洞,並聲稱「前沿AI」(FrontierAI)對於漏洞的發現扮演了關鍵角色。不過,實際發現漏洞的研究人員表示,他們使用的是一般大眾也能取得的AI模型。
網路安全公司Calif在部落格文章中表示,該公司8月1日在大型語言模型的協助下發現這些漏洞,接著便持續投入修補工作。Alphabet旗下的網路安全公司Wiz也在部落格文章中表示,該公司同樣發現了這些漏洞,所使用的是旗下自主式AI漏洞研究工具Wiz Atlas,以及Google的Gemini 4 Argon和OpenAI的GPT-5.6 Sol。
Wiz指出,這些漏洞隱藏在PHP程式碼中超過10年,人類駭客若要利用它來攻擊,技術難度將極高。
網路基礎設施專家米哈烏.沃茲尼亞克表示:「這項漏洞將引發大量自動化攻擊」。他指出,此漏洞可能讓加密貨幣挖礦業者利用有安全弱點的伺服器,在未經授權的情況下使用他人的運算資源進行挖礦。
他也表示,大型犯罪組織及俄羅斯國家級駭客可能利用這些有漏洞的網站作為跳板,發動分散式阻斷服務攻擊(DDoS)及其他網路攻擊。
沃茲尼亞克指出,這起事件凸顯網際網路基礎設施長久以來狀況很差。隨著AI模型能力不斷提升,這些問題逐漸浮上檯面,但實際上早已存在多年。研究人員發現的底層安全漏洞,甚至已有數十年歷史。
他說:「這是整個產業環境的問題,因為業界有強烈誘因追求快速開發與修改」。「企業有誘因迅速部署系統,之後卻再也不更新,也不考慮維護問題」。
KioskNews shows a cleaned-up reading view extracted from the publisher’s page — the original always lives on their site, not ours.